Saudi Arabia Security as a Service Market Size, Share, Trends and Forecast by Component, Organization Size, Application, Vertical, and Region, 2026-2034
Saudi Arabia Security as a Service Market Size, Share, Trends & Forecast (2026-2034)
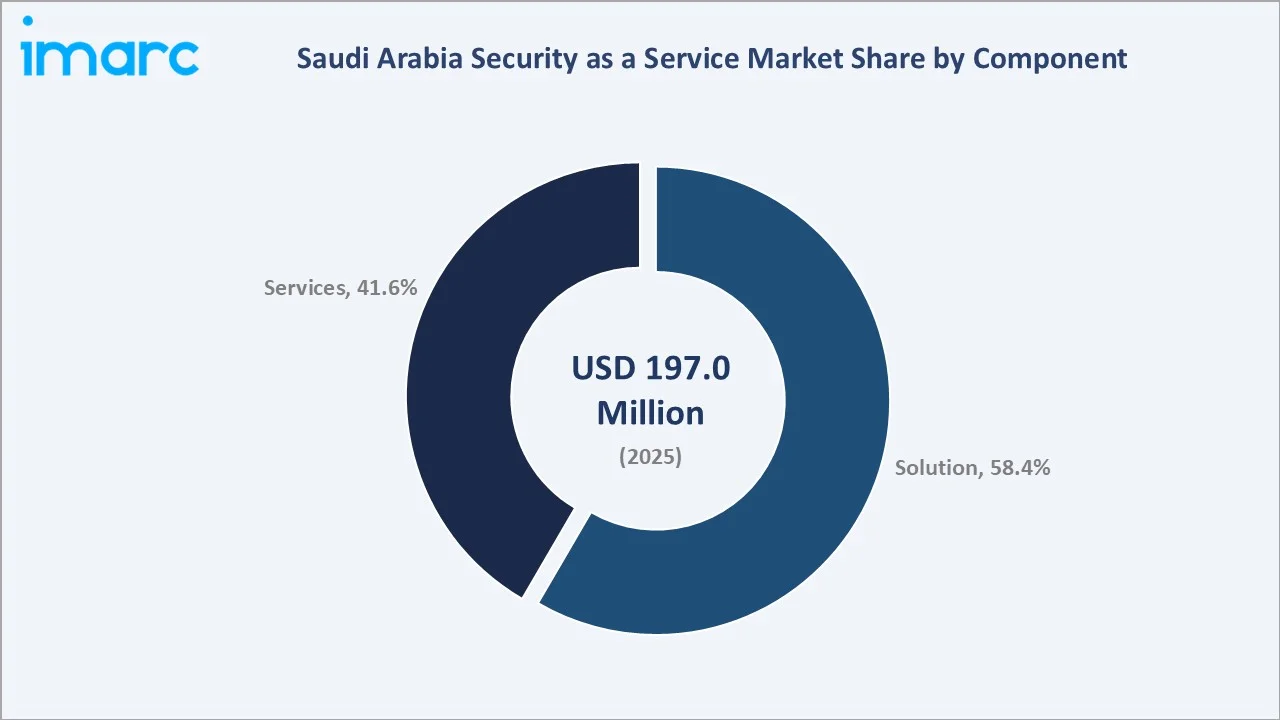
The Saudi Arabia Security as a Service market grew from USD 197.0 Million in 2025 to USD 221.1 Million in 2026 and is projected to reach USD 557.6 Million by 2034, growing at a CAGR of 12.26% during 2026-2034. The market is driven by accelerating cloud adoption across banking, energy, and government sectors, and the large-scale digital infrastructure demands of Vision 2030 mega-projects. The National Cybersecurity Authority launched its licensing system for managed Security Operations Center (MSOC) providers in August 2024, a development that is directly accelerating the formalization and growth of Security as a Service adoption across Saudi enterprises. Solution leads at 58.4% by component, large enterprises dominate at 62.7% by organization size, and the Northern and Central region commands the largest regional share at 45.3% in 2025.
Market Snapshot
|
Metric |
Value |
|
Base Year Market Size (2025) |
USD 197.0 Million |
|
Market Size (2026) |
USD 221.1 Million |
|
Forecast Market Size (2034) |
USD 557.6 Million |
|
CAGR (2026-2034) |
12.26% |
|
Base Year |
2025 |
|
Historical Period |
2020-2025 |
|
Forecast Period |
2026-2034 |
|
Dominant Component |
Solution (58.4%, 2025) |
|
Dominant Organization Size |
Large Enterprises (62.7%, 2025) |
|
Leading Region |
Northern and Central Region (45.3%, 2025) |
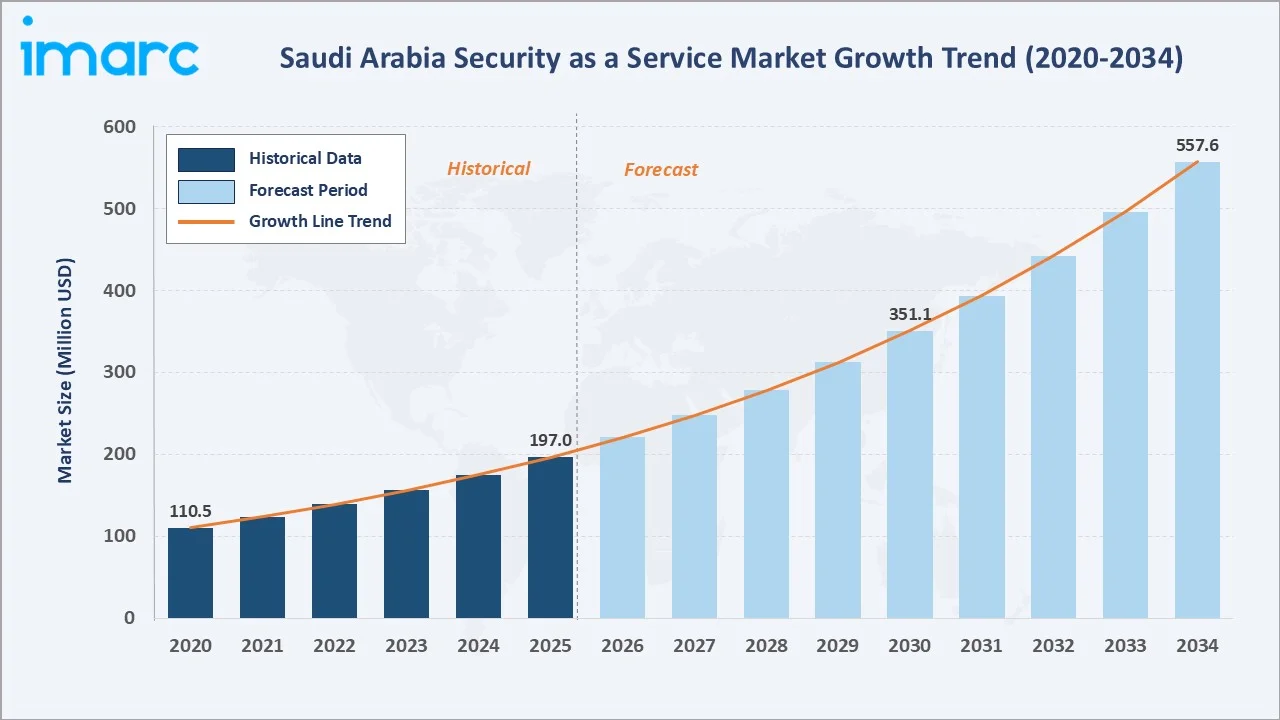
The Saudi Arabia Security as a Service market grew from USD 110.5 Million in 2020 to USD 197.0 Million in 2025, and further to USD 221.1 Million in 2026, reflecting rapid adoption driven by escalating cyber threats, regulatory mandates, and the proliferation of cloud and IoT infrastructure across government and critical industries. The market is projected to reach USD 351.1 Million by 2030 before reaching USD 557.6 Million by 2034.
To get more information on this market, Request Sample
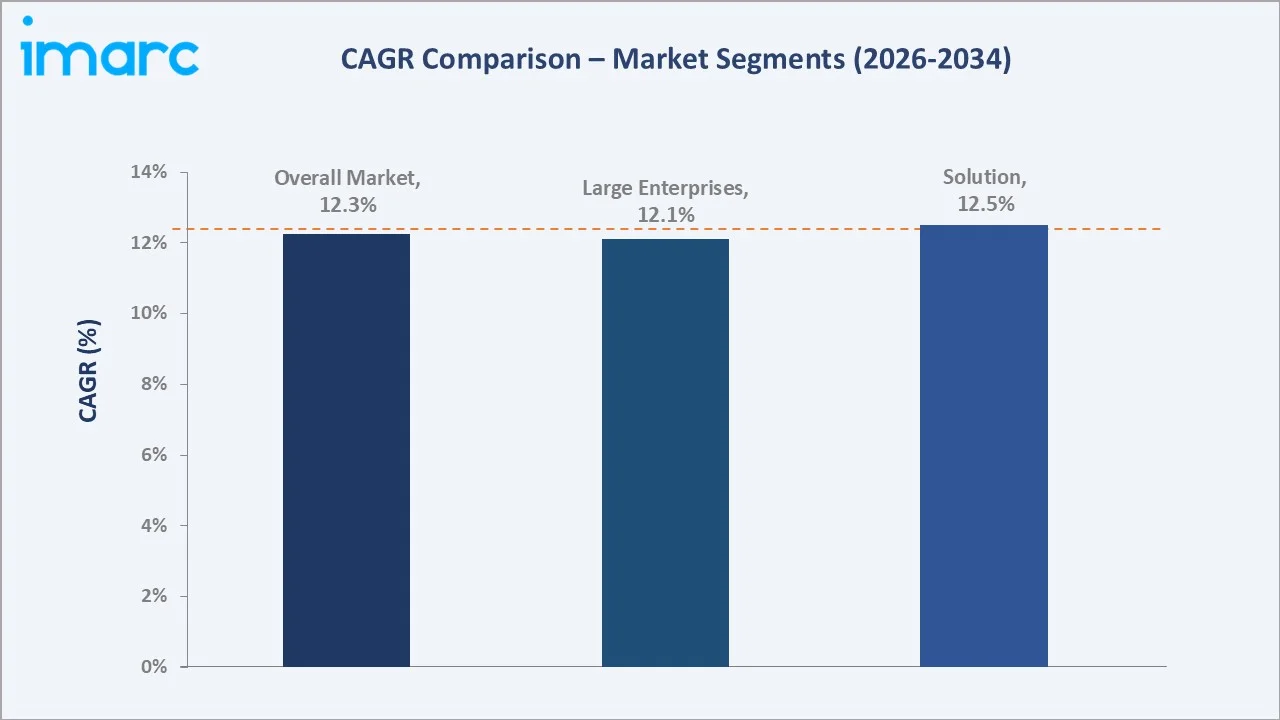
Solutions are growing at a 12.5% CAGR as cloud-native security platforms, including SIEM-as-a-Service, EDR-as-a-Service, and CASB solutions, become the standard procurement model for Saudi enterprises undergoing digital transformation. Large enterprises at 12.1% CAGR reflect sustained investment from government entities, financial institutions, energy companies, and NEOM-linked organizations in comprehensive managed security programs.
Executive Summary
The Saudi Arabia Security as a Service market is experiencing high-velocity growth, driven by the convergence of the most comprehensive cybersecurity regulatory regime in the MENA region, Vision 2030 digital transformation creating vast new attack surfaces across smart cities, cloud platforms, and IoT ecosystems, and an escalating threat landscape requiring organizations to deploy continuous monitoring capabilities that on-premises security models cannot efficiently provide.
Solution at 58.4% leads by component, encompassing cloud-native security platforms delivering network security, endpoint detection and response, application security, cloud access security broker, and identity management as subscription services. Large enterprises lead at 62.7% by organization size, reflecting the high regulatory compliance burden on government agencies, financial institutions, energy companies, and critical infrastructure operators that must demonstrate regulatory compliance. The Northern and Central region leads at 45.3%, anchored by Riyadh as the national capital hosting government ministries, NCA headquarters, financial institutions, and the technology companies providing SECaaS to national clients.
Key Market Insights
|
Insight |
Data |
|
Dominant Component |
Solution - 58.4% share (2025) |
|
Dominant Organization Size |
Large Enterprises - 62.7% share (2025) |
|
Leading Region |
Northern and Central Region - 45.3% (2025) |
|
Key Market Opportunity |
Rising cloud adoption, Vision 2030-driven digital transformation, growing SME cybersecurity needs, AI-powered threat detection, expanding IoT deployments, increasing demand for managed security services, and the development of localized cybersecurity capabilities |
Key Analytical Observations Supporting the Above Data:
- Solution at 58.4%: SECaaS solutions lead because cloud-native security platforms deliver the scalable, always-updated protection that static on-premises security tools cannot provide against dynamic threat actors.
- Large Enterprises at 62.7%: Large enterprises dominate because government entities, financial institutions, energy companies, telecom operators, and critical infrastructure providers face the most intensive compliance requirements, the highest cyber threat exposure from state-sponsored actors targeting Saudi national infrastructure, and the budgetary capacity to deploy comprehensive managed security programs.
- Northern and Central Region at 45.3%: Riyadh dominance reflects its position as the seat of government policy driving mandatory compliance, the headquarters location of regulatory bodies setting cybersecurity requirements, and the concentration of financial sector institutions requiring cybersecurity framework compliance.
Saudi Arabia Security as a Service Market Overview
The Saudi Arabia Security as a Service market encompasses the subscription-based delivery of cybersecurity capabilities through cloud infrastructure, eliminating the requirement for organizations to own and operate on-premises security hardware. Core service categories include Security Information and Event Management as a Service (SIEM-aaS), Managed Detection and Response (MDR), Endpoint Detection and Response as a Service (EDR-aaS), Cloud Access Security Broker (CASB), Distributed Denial of Service protection (DDoS-aaS), Vulnerability Management as a Service (VMaaS), Identity and Access Management as a Service (IAM-aaS), and Web Application Firewall as a Service (WAF-aaS). These are delivered across network security, endpoint security, application security, cloud security, and identity security application domains.
Market Dynamics
To evaluate market opportunities, Request Sample
Market Drivers
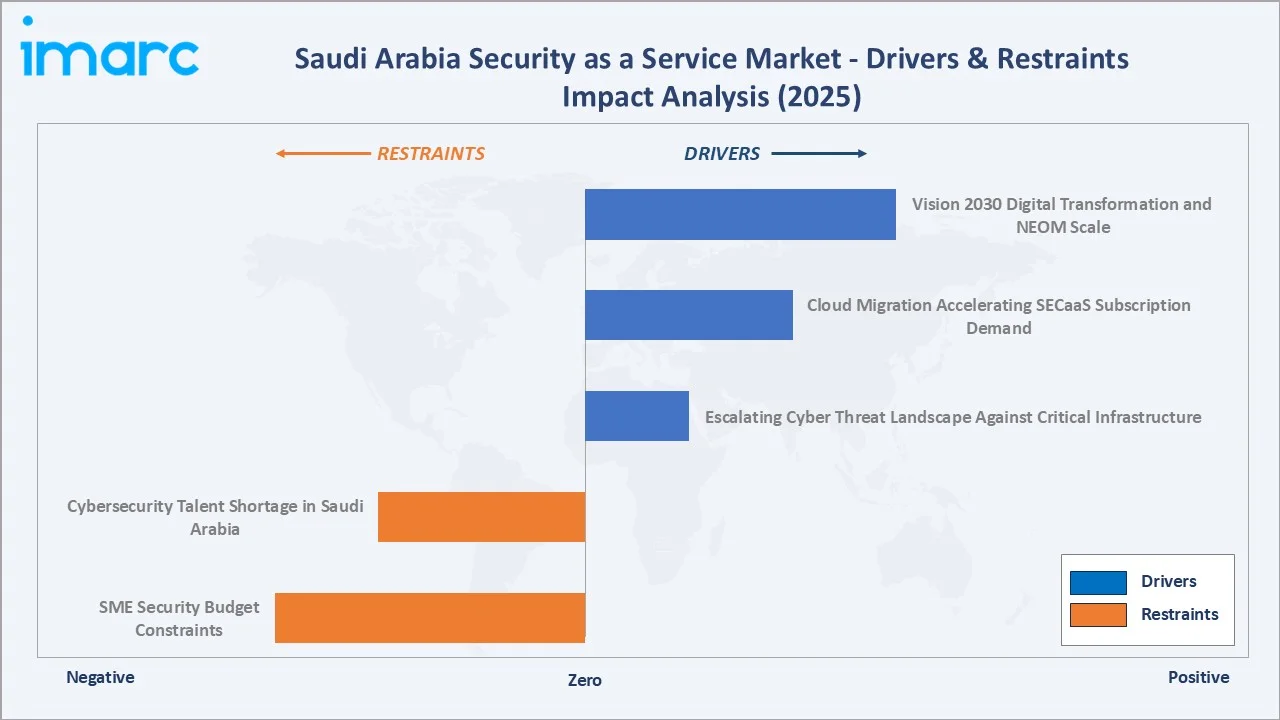
- Vision 2030 Digital Transformation and NEOM Scale: Saudi Arabia Vision 2030 digital economy initiatives are creating vast new cybersecurity attack surfaces across smart city infrastructure, cloud government platforms, and hyperconnected IoT ecosystems. NEOM alone has deployed AI engines capable of analyzing millions of security events per second, representing the most demanding security monitoring requirement in the Saudi market. Saudi Arabia’s cybersecurity annual spending surpassed SAR 15 billion by 2025, with structural shifts toward hyperscale cloud deployments and smart cities completely changing specialized procurement cycles that benefit SECaaS providers.
- Cloud Migration Accelerating SECaaS Subscription Demand: The increasing shift toward cloud infrastructure across banking, energy, and industrial sectors is increasing demand for scalable cloud-based security solutions. Saudi Arabia national digital transformation initiatives, growing adoption of Software-as-a-Service and Infrastructure-as-a-Service, and hyperscale cloud investments are creating the cloud-native workload base that SECaaS is designed to protect.
- Escalating Cyber Threat Landscape Against Critical Infrastructure: The rising frequency and sophistication of cyberattacks targeting Saudi Arabia’s critical infrastructure are increasing the need for continuous security monitoring and threat detection. Energy, utilities, transportation, and other essential sectors are strengthening their cybersecurity defenses to reduce operational and data-related risks. This is encouraging organizations to outsource specialized security functions to Security as a Service providers.
Market Restraints
- Cybersecurity Talent Shortage in Saudi Arabia: Saudi Arabia faces a significant shortage of qualified cybersecurity professionals that constrains both the development of domestic SECaaS capabilities and the client-side ability to effectively manage and configure complex SECaaS platforms. While SECaaS is partly a response to this skills gap, talent scarcity at providers limits service expansion capacity and creates wage inflation that compresses provider margins.
- SME Security Budget Constraints: Despite the NCA compliance mandate applying progressively to smaller organizations, small and medium-sized enterprises face budget constraints that limit their ability to procure comprehensive SECaaS solutions. The 37.3% SME market share relative to 62.7% large enterprise share reflects the current affordability gap, though the SME segment represents the largest growth opportunity as compliance requirements expand and tiered pricing models enable more accessible SECaaS options.
Market Opportunities
- NEOM and Giga-Project Security Infrastructure Demand: NEOM, The Line, Diriyah Gate, Qiddiya, and other Vision 2030 giga-projects represent a concentrated, high-value SECaaS opportunity as these hyperconnected smart infrastructure projects require AI-driven security monitoring from inception. Tonomus has deployed AI engines in NEOM capable of analyzing millions of security events per second, establishing the technical requirement baseline for SECaaS providers seeking to serve giga-project security mandates at unprecedented monitoring scale.
- AI-Powered Security Analytics and Autonomous Response: The integration of artificial intelligence and machine learning into SECaaS platforms, enabling behavioral anomaly detection, automated threat correlation, and autonomous incident response, creates premium product tier opportunities for SECaaS providers.
Market Challenges
- High Implementation and Subscription Costs: Security as a Service requires organizations to allocate recurring budgets for subscriptions, integration, monitoring, and technical support. Smaller enterprises may find the overall cost challenging, particularly when multiple security services are required. Integration with existing legacy systems can further increase implementation expenses. Cost considerations may therefore slow adoption among price-sensitive organizations.
- Integration with Legacy IT Infrastructure: Many organizations operate a combination of legacy systems, on-premises infrastructure, and newer cloud platforms. Integrating Security as a Service solutions across these heterogeneous environments can be technically complex. Compatibility issues may require additional customization and professional services. This can increase deployment time and affect the overall adoption process.
Emerging Market Trends
1. Growth of Locally Hosted Cybersecurity SaaS
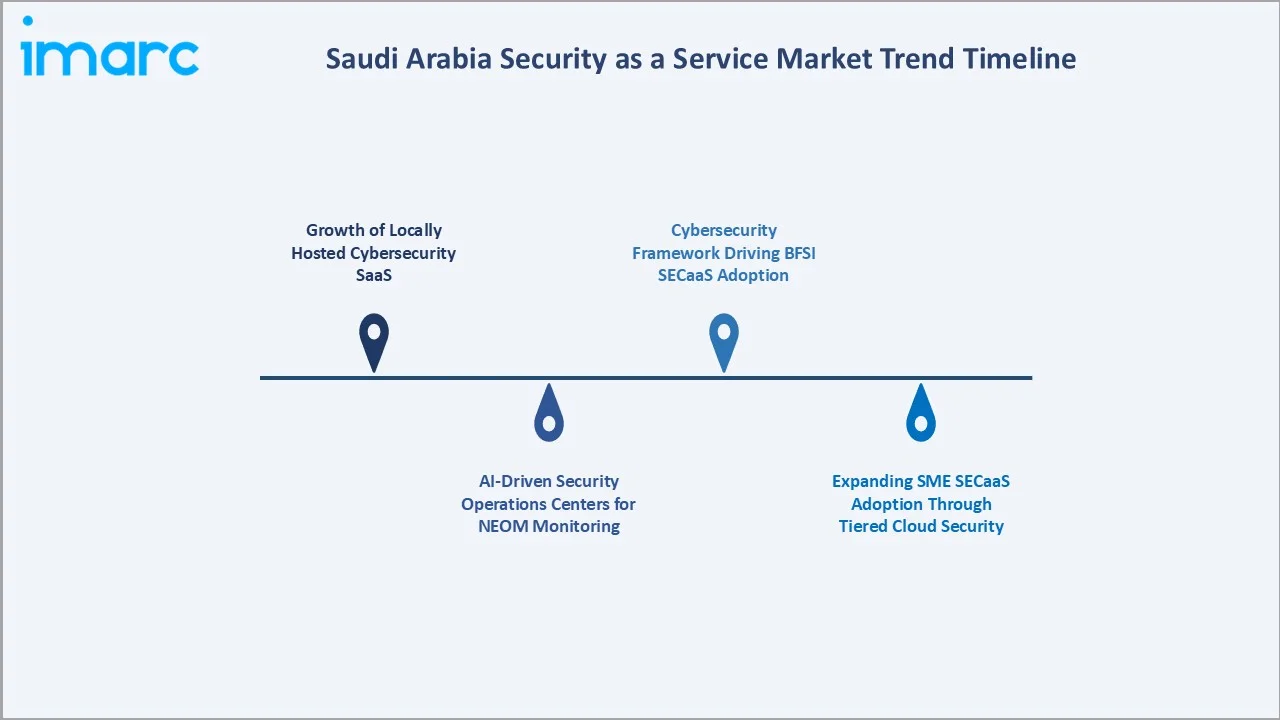
In July 2025, Black Duck Software, Inc. strengthened its presence in Saudi Arabia with the launch of the Black Duck Polaris Platform. The company has introduced what it describes as the first application security Software as a Service (SaaS) platform hosted within the Kingdom, reinforcing its focus on delivering locally hosted application security solutions to the Saudi market. The launch highlights a growing trend toward locally hosted Security as a Service solutions in Saudi Arabia, particularly for organizations requiring greater control over sensitive application and security data. Local hosting can also support data-residency requirements and encourage adoption of cloud-based cybersecurity services among enterprises.
2. AI-Driven Security Operations Centers for NEOM Monitoring
NEOM's deployment of AI engines capable of analyzing millions of security events per second establishes the most demanding SECaaS monitoring requirement in Saudi Arabia and sets the technology benchmark for smart city security monitoring that will progressively apply across other Vision 2030 smart infrastructure projects. The cloud security market in Saudi Arabia is growing as multi-cloud environments proliferate, with cloud security posture management showing early growth dynamics driven by the complexity of securing NEOM and other giga-project multi-cloud architectures that cannot be monitored through traditional SIEM approaches.
3. Cybersecurity Framework Driving BFSI SECaaS Adoption
The Saudi Central Bank Cybersecurity Framework imposes specific security controls on banks, insurance companies, and financial market infrastructure that align with and reinforce requirements for the financial sector. SAMA-regulated financial institutions are among the highest-value SECaaS clients in Saudi Arabia, requiring comprehensive continuous monitoring, identity and access management, and real-time fraud detection capabilities.
4. Expanding SME SECaaS Adoption Through Tiered Cloud Security
Rising cloud migration risks are accelerating commercial intake of scalable SECaaS models among regional small and medium enterprises. Cloud-native SECaaS with tiered pricing, from essential compliance monitoring through to comprehensive MDR, is progressively making enterprise-grade security capabilities accessible to the SME segment currently at 37.3% market share.
Industry Value Chain Analysis
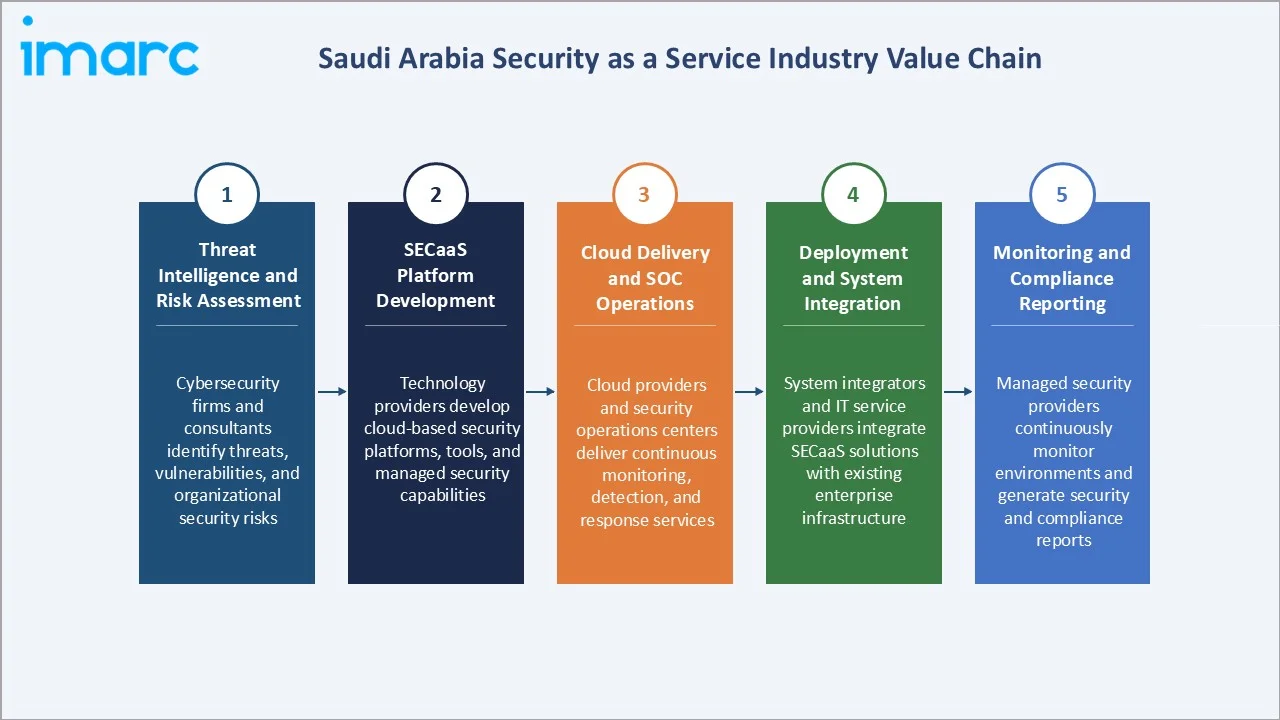
The Saudi Arabia Security as a Service value chain spans five integrated stages from threat intelligence development through continuous monitoring and compliance reporting. The cloud delivery and SOC operations stage captures the highest operational value in the chain, as the continuous multi-client security monitoring, alert triage, threat investigation, and incident response activities that licensed managed SOC providers deliver represent the core service that Saudi enterprises pay for and that the licensing framework specifically regulates.
|
Stage |
Key Participants |
|
Threat Intelligence and Risk Assessment |
Cybersecurity firms and consultants identify threats, vulnerabilities, and organizational security risks. |
|
SECaaS Platform Development |
Technology providers develop cloud-based security platforms, tools, and managed security capabilities. |
|
Cloud Delivery and SOC Operations |
Cloud providers and security operations centers deliver continuous monitoring, detection, and response services. |
|
Deployment and System Integration |
System integrators and IT service providers integrate SECaaS solutions with existing enterprise infrastructure. |
|
Monitoring and Compliance Reporting |
Managed security providers continuously monitor environments and generate security and compliance reports. |
The cloud delivery and SOC operations stage is the highest value-added stage in the SECaaS value chain. Licensed SOC operators who maintain certified Saudi Arabia-based security operations facilities, continuous analyst staffing, and demonstrated compliance with quality and maturity standards command sustained pricing power and preferred vendor positioning in a compliance-driven market where regulatory credentials are prerequisites for procurement consideration.
Technology Landscape in the Saudi Arabia Security as a Service Industry
AI-Powered Security Information and Event Management
Modern SIEM-as-a-Service platforms deployed in Saudi Arabia combine artificial intelligence and machine learning for behavioral analytics, user and entity behavior analytics, and automated alert correlation that reduce the false positive rates overwhelming analyst capacity at traditional rule-based SIEM deployments. The analytical capability to process millions of security events per second, as demonstrated in the NEOM deployment, sets the performance baseline for next-generation SIEM-aaS in Saudi Arabia.
Zero Trust Network Access and Cloud-Native Security
Zero trust architecture, verifying every user, device, and network request regardless of location or previous authentication, is becoming the security model of choice for Saudi Arabia enterprises migrating workloads to cloud environments where traditional perimeter-based security is architecturally insufficient. Key cloud-native zero trust SECaaS platforms are being deployed by Saudi financial institutions, government agencies, and large enterprises, aligning with regulatory requirements for identity-centric access controls across hybrid multi-cloud environments.
Operational Technology Security Monitoring
The convergence of IT and OT environments across Saudi Arabia energy, manufacturing, and utilities sectors is creating demand for specialized SECaaS capabilities that extend threat monitoring from IT networks into industrial control systems, SCADA platforms, and connected infrastructure. OT security products are being deployed in critical infrastructure environments under the regulatory requirements for critical infrastructure protection, creating a growing OT SECaaS opportunity that requires specialized monitoring capabilities beyond standard IT security platforms.
Market Segmentation Analysis
The report covers the following segments:
|
Segment Category |
Leading Segment |
Market Share |
Year |
|
Component |
Solution |
58.4% |
2025 |
|
Organization Size |
Large Enterprises |
62.7% |
2025 |
|
Application |
🔒 |
🔒 |
2025 |
|
Vertical |
🔒 |
🔒 |
2025 |
|
Region |
Northern and Central Region |
45.3% |
2025 |

By Component
Solutions lead at 58.4% in 2025, reflecting the dominant commercial weight of cloud-delivered security platform subscriptions across network security-as-a-service, endpoint detection and response, SIEM-as-a-service, CASB, identity and access management, and application security testing services. Solution revenue concentration is driven by enterprise-scale subscription contracts for comprehensive security platforms that command multi-year total contract values substantially larger than individual professional services or training engagements.
To access detailed market analysis, Request Sample
Services at 41.6% encompass professional services including security architecture consulting, technical implementation and SOC setup, managed security services including continuous SOC monitoring and MDR, and training and capability development programs.
By Organization Size
Large enterprises lead at 62.7% in 2025, reflecting the intensive cybersecurity investment by government ministries, financial institutions subject to regulatory framework requirements, energy companies including Saudi Aramco, telecom operators, and critical infrastructure providers that face the most comprehensive compliance obligations.
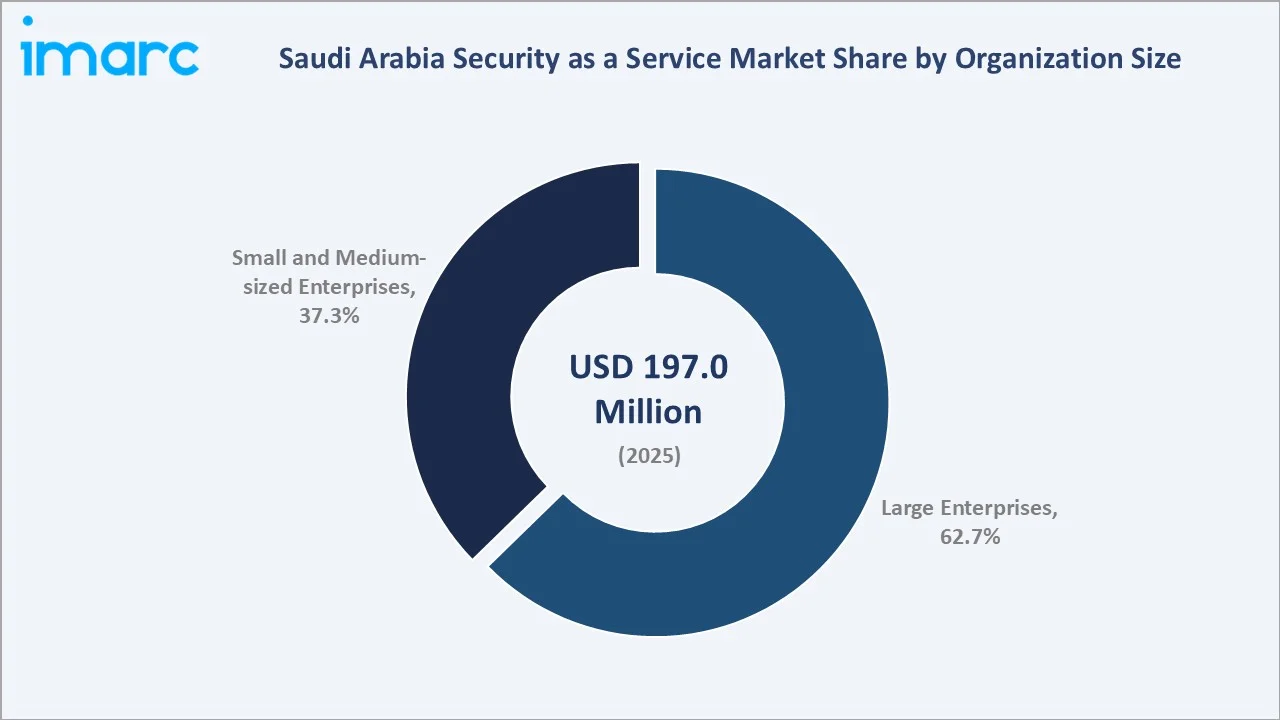
Small and medium-sized enterprises at 37.3% represent the fastest-growing organizational segment as regulatory compliance requirements progressively expand to smaller organizations and cloud-native tiered SECaaS pricing makes enterprise security capabilities accessible to organizations without dedicated security teams.
Regional Market Insights
|
Region |
Share (2025) |
Key Saudi Arabia Security as a Service Market Drivers & Characteristics |
|
Northern and Central Region |
45.3% |
High concentration of enterprises, government institutions, and digital infrastructure supports demand for managed cybersecurity services. |
|
Eastern Region |
24.6% |
Strong presence of energy, industrial, and critical infrastructure organizations drives cybersecurity and monitoring requirements. |
|
Western Region |
20.1% |
Growing commercial, tourism, and technology activities are supporting adoption of cloud-based security solutions. |
|
Southern Region |
10.0% |
Increasing digitalization among businesses and public-sector organizations is gradually creating demand for SECaaS solutions. |
The Northern and Central region accounted for the largest share of the Saudi Arabia Security as a Service market, representing 45.3% in 2025, supported by the concentration of enterprises, government institutions, and digital infrastructure. The Eastern region held a 24.6% share, driven by the presence of energy, industrial, and critical infrastructure organizations.
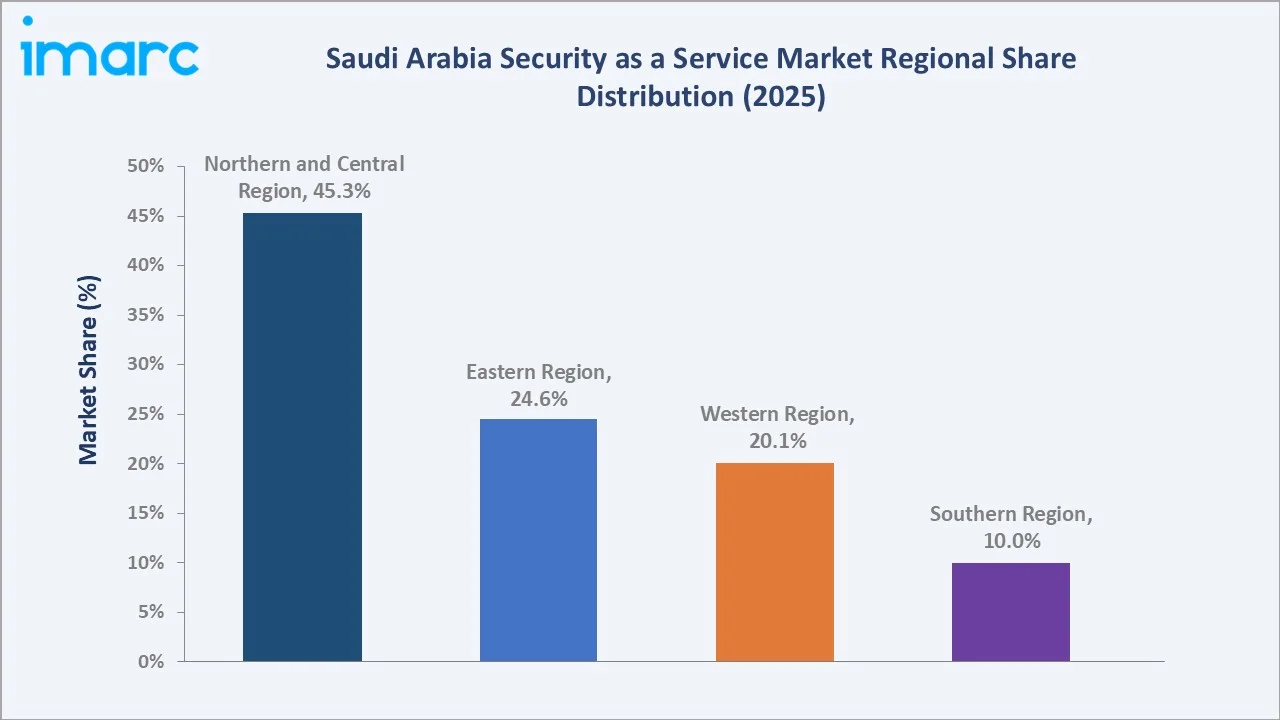
The Western region contributed 20.1%, with commercial, tourism, and technology activities supporting cybersecurity adoption. The Southern region accounted for the remaining 10.0%, reflecting increasing digitalization among businesses and public-sector organizations.
Competitive Landscape
The Saudi Arabia Security as a Service market is served by a combination of global technology companies delivering cloud-native security platforms and locally licensed Saudi Arabia-based SOC operators that combine international technology with compliant in-Kingdom service delivery.
|
Company |
Key Offerings |
Market Position |
Core Strength |
|
Palo Alto Networks |
Prisma Access, Cortex XDR, Cortex Cloud |
Market Leader |
Palo Alto Networks provides local cloud infrastructure and AI-driven security platforms in Saudi Arabia to support domestic data residency and align with national digital transformation goals. |
|
Cisco Systems, Inc. |
Cisco Umbrella, Cisco Talos, Cisco XDR |
Market Leader |
Cisco Systems, Inc. provides agile, cloud-delivered security infrastructure and localized data centers in Saudi Arabia to support the Kingdom's digital transformation under Vision 2030. |
|
sirar by stc |
sirar MDR, Secure Access Service Edge (SASE) |
Established Player |
sirar by stc serves as a leading national Managed Security Service Provider (MSSP) in Saudi Arabia, delivering robust Security as a Service (SECaaS) models to protect critical infrastructure. |
|
Fortinet, Inc. |
FortiSASE, FortiEDR, FortiSIEM, FortiSOAR |
Innovator |
Fortinet, Inc. delivers cloud-delivered and managed Security-as-a-Service (SECaaS) capabilities in Saudi Arabia through its FortiSASE, SOCaaS, and Security frameworks to secure hybrid workforces and cloud transformations. |
The mandatory licensing requirement has fundamentally reshaped competitive dynamics by requiring international vendors without Saudi Arabia-based SOC infrastructure to partner with locally licensed MSSPs for compliant service delivery. This creates a structural competitive advantage whose domestic SOC investments now serve as market access prerequisites for international technology vendors seeking Saudi Arabia clients.
Key Company Profiles
Palo Alto Networks
Palo Alto Networks is a global cybersecurity company providing network, cloud, endpoint, and application security solutions. In the Saudi Arabia Security as a Service market, the company supports organizations with cloud-delivered security capabilities and managed protection solutions. Its portfolio includes technologies for threat prevention, security monitoring, access management, and incident response. The company serves enterprises and organizations across sectors seeking to strengthen cybersecurity and protect digital infrastructure.
- Key Offerings: Prisma Access, Cortex XDR, Cortex Cloud.
- Strategic Focus: Expanding cloud-delivered cybersecurity capabilities and strengthening protection across network, cloud, endpoint, and application environments. In Saudi Arabia, the company emphasizes advanced threat prevention, integrated security platforms, and solutions aligned with organizations’ evolving digital security requirements.
Cisco Systems, Inc.
Cisco Systems, Inc. is a global technology company providing networking, cybersecurity, cloud, and collaboration solutions. In the Saudi Arabia Security as a Service market, Cisco supports organizations with security technologies covering network protection, threat detection, secure access, and cloud environments. Its portfolio enables enterprises to integrate cybersecurity capabilities across distributed IT infrastructures. The company serves businesses and institutions across sectors seeking to strengthen their digital networks and security posture.
- Key Offerings: Cisco Umbrella, Cisco Talos, Cisco XDR.
- Strategic Focus: Expanding integrated, cloud-delivered cybersecurity capabilities across network, endpoint, and access environments. In Saudi Arabia, the company emphasizes secure digital transformation through solutions that support threat detection, secure connectivity, and centralized security management.
Market Concentration Analysis
The Saudi Arabia Security as a Service market has moderate concentration in the large enterprise and government segment serving the majority of high-value accounts, while the emerging SME segment is more fragmented with numerous regional and domestic providers competing on price and compliance simplicity. Global technology vendors increasingly depend on locally licensed partnerships, creating a complementary market structure where technology vendors and licensed SOC operators are more likely to partner than compete directly.
Market concentration is expected to evolve through 2034 as the market grows at 12.26% CAGR and new international vendors establish Saudi Arabia-based operations to qualify for licensing, while the SME segment expands with new domestic entrants offering compliance-focused tiered pricing. The government's cybersecurity investments may support development of additional domestic SECaaS capability, potentially creating new Saudi-owned providers competing alongside established international and regional players.
Investment & Growth Opportunities
Highest Growth Segments
SME SECaaS expansion represents the largest volume growth opportunity as NCA compliance requirements extend and tiered pricing makes enterprise security accessible to the private sector SME employment base.
Investment Themes
- AI-Driven Security Analytics for Giga-Project Scale: Investment in AI-powered security analytics platforms capable of processing millions of security events per second positions providers for the highest-value contract opportunities across NEOM, The Line, Qiddiya, and other Vision 2030 smart infrastructure projects requiring next-generation monitoring at unprecedented scale.
- SME SECaaS Tiered Product Development: Developing cloud-delivered SECaaS packages priced and featured for Saudi Arabia SME budgets and compliance requirements represents the largest addressable market expansion opportunity, with automated compliance reporting against regulatory controls providing the primary value proposition for SMEs without dedicated security staff.
Future Market Outlook (2026-2034)
The Saudi Arabia Security as a Service market stood at USD 197.0 Million in 2025 and is projected to grow from USD 221.1 Million in 2026 to USD 557.6 Million by 2034, exhibiting a CAGR of 12.26% during the forecast period. The market is expected to reach an intermediate milestone of approximately USD 351.1 Million by 2030, as regulatory compliance programs reach full private sector penetration, NEOM and giga-project security monitoring infrastructure scales to operational phase requirements, and the SME segment transitions from compliance awareness to structured SECaaS adoption under expanded enforcement.
Three structural forces will define Saudi Arabia Security as a Service market through 2034. First, the regulatory architecture creates a compliance-driven SECaaS procurement engine that operates independently of economic cyclicality. Second, Vision 2030 digital infrastructure investment will sustain above-market SECaaS demand growth through peak digital transformation delivery between 2026 and 2030, when the largest volume of Vision 2030 digital infrastructure comes online and requires security monitoring. Third, Saudi Arabia ongoing establishment as the MENA cybersecurity benchmark will attract continued international SECaaS vendor investment in Saudi Arabia operations, creating a competitive landscape that progressively improves service quality, expands product innovation, and enables market expansion into currently underserved SME and Southern Region segments through 2034.
Research Methodology
Primary Research
Primary research comprised structured consultations with IT security managers at Saudi government entities and financial institutions, licensing compliance consultants, SECaaS vendor representatives in Saudi Arabia, SOC operations managers, cybersecurity procurement specialists, and industry association members representing the Saudi Arabia technology sector. These discussions validated market sizing, assessed the commercial impact of mandatory SOC licensing, identified cloud migration security demand dynamics, and provided competitive intelligence on vendor positioning and contract structures across major client segments.
Secondary Research
Secondary research drew on IMARC Group market data, regulatory publications, Saudi Arabia managed security services market reports, Saudi Arabia cybersecurity and MSSP market analysis, Sovereign Magazine analysis of regulatory impact on procurement, Digital Competitiveness Report cybersecurity readiness ranking, and company investor relations materials.
Forecasting Models
Market forecasts incorporated regulatory compliance mandate expansion timeline modeling across government, large enterprise, and SME segments, Vision 2030 giga-project digital infrastructure deployment schedule and associated security monitoring demand projections, cloud migration rate projections for Saudi Arabia financial services and energy sectors, SME SECaaS adoption rate projections as tiered pricing reduces entry barriers, and macroeconomic indicators including Saudi Arabia non-oil GDP growth through 2034.
Saudi Arabia Security as a Service Market Report Coverage:
| Report Features | Details |
|---|---|
| Base Year of the Analysis | 2025 |
| Historical Period | 2020-2025 |
| Forecast Period | 2026-2034 |
| Units | Million USD |
| Scope of the Report |
Exploration of Historical Trends and Market Outlook, Industry Catalysts and Challenges, Segment-Wise Historical and Future Market Assessment:
|
| Components Covered | Solution, Services |
| Organization Sizes Covered | Small and Medium-sized Enterprises, Large Enterprises |
| Applications Covered | Network Security, Endpoint Security, Application Security, Cloud Security, Others |
| Verticals Covered | BFSI, Government and Defense, Retail and E-Commerce, Healthcare and Life Sciences, IT and Telecom, Energy and Utilities, Manufacturing, Others |
| Regions Covered | Northern and Central Region, Western Region, Eastern Region, Southern Region |
| Companies Covered | Palo Alto Networks, Cisco Systems, Inc., sirar by stc, Fortinet, Inc., etc. |
| Customization Scope | 10% Free Customization |
| Post-Sale Analyst Support | 10-12 Weeks |
| Delivery Format | PDF and Excel through Email (We can also provide the editable version of the report in PPT/Word format on special request) |
Key Benefits for Stakeholders:
- IMARC’s industry report offers a comprehensive quantitative analysis of various market segments, historical and current market trends, market forecasts, and dynamics of the Saudi Arabia security as a service market from 2020-2034.
- The research report provides the latest information on the market drivers, challenges, and opportunities in the Saudi Arabia security as a service market.
- Porter's five forces analysis assist stakeholders in assessing the impact of new entrants, competitive rivalry, supplier power, buyer power, and the threat of substitution. It helps stakeholders to analyze the level of competition within the Saudi Arabia security as a service industry and its attractiveness.
- Competitive landscape allows stakeholders to understand their competitive environment and provides an insight into the current positions of key players in the market.
Frequently Asked Questions About the Saudi Arabia Security as a Service Market Report
The Saudi Arabia Security as a Service market reached USD 221.1 Million in , driven by mandatory SOC licensing compliance, Vision 2030 digital transformation creating new security requirements, cloud migration in financial services and energy sectors, and the escalating threat landscape requiring continuous monitoring capabilities.
The market is projected to grow at a CAGR of 12.26% during 2026-2034, supported by regulatory compliance mandates with penalties, Vision 2030 cybersecurity investments, hyperscale cloud investments, NEOM AI security monitoring requirements, and expanding SME SECaaS adoption.
The market is projected to reach approximately USD 351.1 Million by 2030, as regulatory compliance programs reach full private sector penetration, NEOM and giga-project security monitoring scales to operational phase, and the SME segment transitions to structured SECaaS adoption under expanded NCA enforcement and tiered pricing models.
Solution leads with a 58.4% share in 2025, reflecting the dominant commercial weight of cloud-native security platform subscriptions that collectively deliver the continuous monitoring and compliance management capabilities Saudi enterprises require under regulatory mandates.
Large enterprises lead with a 62.7% share in 2025, reflecting intensive regulatory framework compliance requirements on government agencies, financial institutions, energy companies, and critical infrastructure operators that face the highest regulatory burden and budgetary capacity for comprehensive managed security programs.
The Northern and Central region leads with a 45.3% share in 2025, anchored by Riyadh as the location of regulatory headquarters, government ministry concentration, financial sector institutions, and the highest density of large enterprise and government SECaaS procurement decisions aligned with Vision 2030 administrative programs.
Key players include Palo Alto Networks, Cisco Systems, Inc., sirar by stc, and Fortinet, Inc., among others.
The market is projected to reach USD 557.6 Million by 2034, driven by full private sector compliance, NEOM and giga-project operational security monitoring at AI scale, SME SECaaS expansion, advanced MDR and zero trust adoption, and Saudi Arabia establishment as the MENA cybersecurity benchmark, attracting continued international SECaaS vendor investment.
Need more help?
- Speak to our experienced analysts for insights on the current market scenarios.
- Include additional segments and countries to customize the report as per your requirement.
- Gain an unparalleled competitive advantage in your domain by understanding how to utilize the report and positively impacting your operations and revenue.
- For further assistance, please connect with our analysts.
 Request Customization
 Speak to an Analyst
 Request Brochure
 Inquire Before Buying
Benefits of Customization
- Personalize this research
- Triangulate with your data
- Get data as per your format and definition
- Gain a deeper dive into a specific application, geography, customer, or competitor
- Any level of personalization
Get in Touch With Us
UNITED STATES
Phone: +1-201-971-6302
INDIA
Phone: +91-120-433-0800
UNITED KINGDOM
Phone: +44-753-714-6104
Email: [email protected]
Client Testimonials























Related Reports

Choose your plan
*Please note that the prices mentioned below are starting prices for each bundle type. Kindly contact our team for further details.*
Single User License
- 1 User License, Access on 2 Devices
- PDF Report + Excel Dataset (Password Protected)
- Lifetime Access
- No Printing Rights
- 10% Free Report Customization
- 10–12 Weeks of Analyst Support
Five User License
- Access for 5 Users, 2 Devices per User
- PDF Report + Excel Dataset (Password Protected)
- Lifetime Access
- Dedicated Account Manager
- 12–14 Weeks of Analyst Support
- No Printing Rights
- 15% Free Report Customization
- 25% Discount on Your Next Purchase
Corporate User License
- Unlimited User Access (Within Your Organization)
- PDF Report + Excel Dataset
- Lifetime Access
- Dedicated Account Manager
- 14–20 Weeks of Analyst Support
- No Printing Rights
- 20% Free Report Customization
- 30% Discount on Your Next Purchase
Essential Insights
What's included:
3 reports
- Lifetime Access
- PDF Reports
- Excel Datasets
- 2 Weeks of Free Analyst Support
- 2 User Licenses
- Access on 2 Devices
- Printing Rights
- Complimentary PowerPoint (PPT) Version
- Complimentary License Upgrade
Professional Access
What's included:
5 reports
- Lifetime Access
- PDF Reports
- Excel Datasets
- 8 Weeks of Free Analyst Support
- 2 User Licenses
- Access on 2 Devices
- Printing Rights
- Complimentary PowerPoint (PPT) Version
- Complimentary License Upgrade
Business Advantage
What's included:
8 reports
- Lifetime Access
- PDF Reports
- Excel Datasets
- 14 Weeks of Free Analyst Support
- 2 User Licenses
- Access on 2 Devices
- Printing Rights
- Complimentary PowerPoint (PPT) Version
- Complimentary License Upgrade
Enterprise Intelligence
What's included:
10 reports
- Lifetime Access
- PDF Reports
- Excel Datasets
- 20 Weeks of Free Analyst Support
- 2 User Licenses
- Access on 2 Devices
- Printing Rights
- Complimentary PowerPoint (PPT) Version
- Complimentary License Upgrade